Once You're Past Reception, Nobody's Checking Anymore
An honest look at applying zero-trust security principles to physical access. Covers what NIST's SP 800-207 standard actually says (and where it stops, at the network layer, not the front door), the growing industry practice of extending "never trust, always verify" to physical security anyway, three zero-trust principles mapped to visitor and contractor access specifically, and where a manual front-desk process structurally can't keep up.


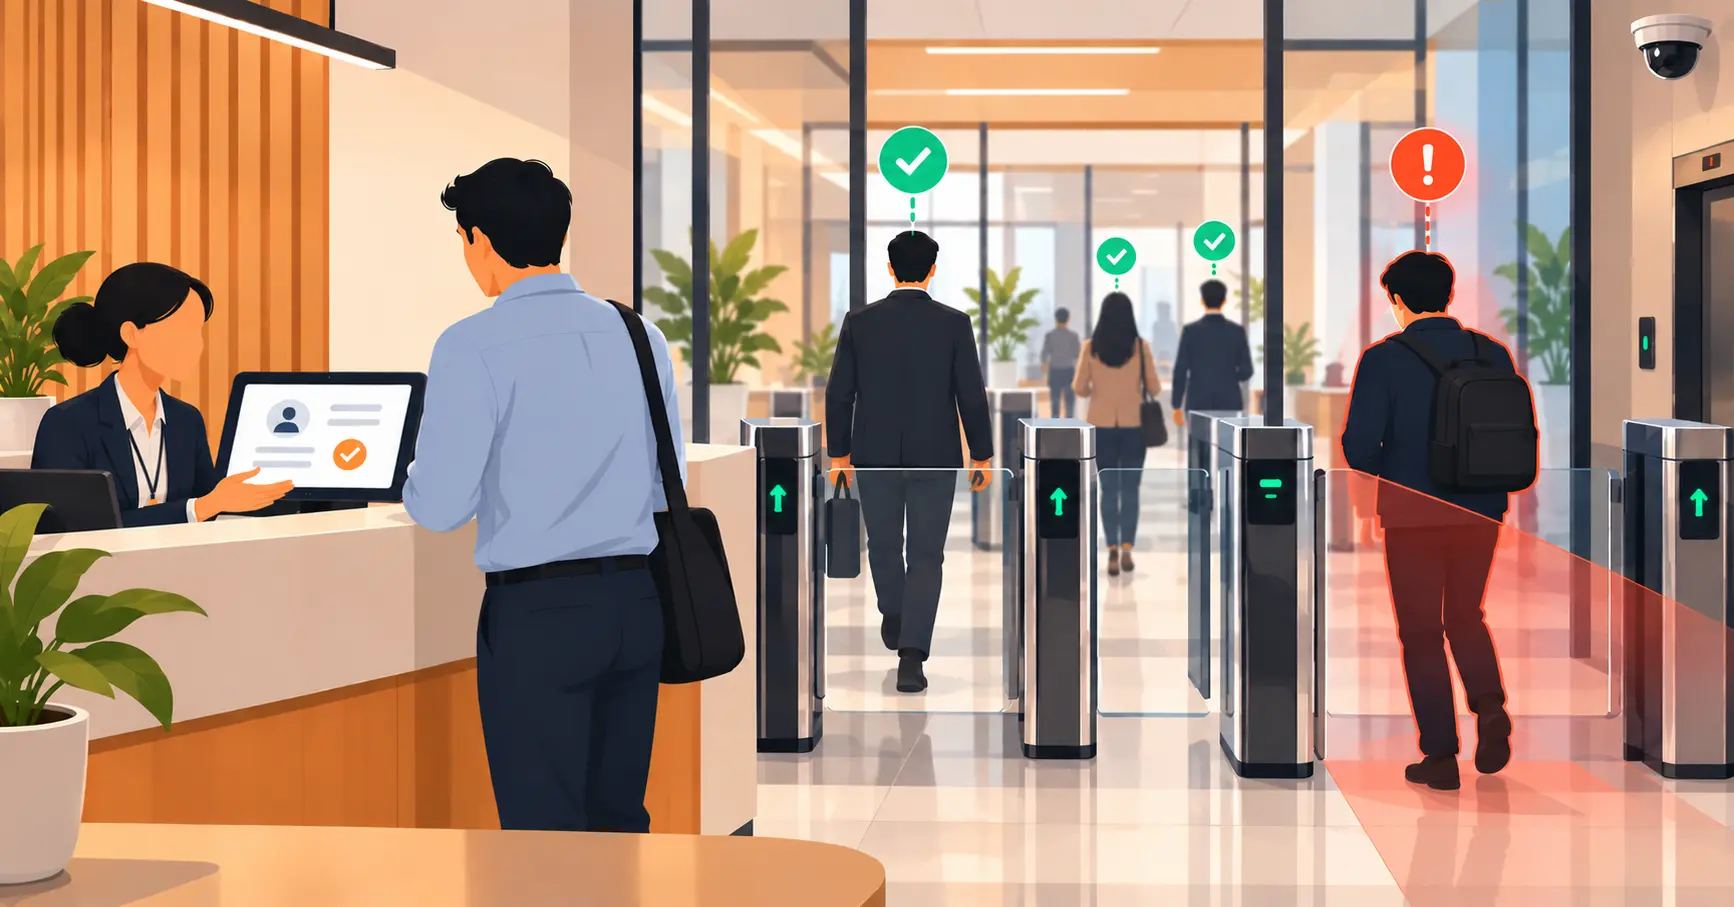
Table of Content
Try Vizitor for Free!
Zero trust is a network security model, built around one rule: never trust, always verify. Nobody gets automatic trust just because of where they are, inside the corporate network, or inside the building. That principle comes from NIST, and NIST built it for digital systems, not front doors. But the same logic exposes something most physical security still gets wrong: once someone’s past reception, most buildings trust them completely, for the rest of their visit, with no further check at all.
What Zero Trust Actually Means
NIST’s SP 800-207 defines zero trust architecture for enterprise IT: identity, endpoints, and network resources. Its central idea is that physical or network location shouldn’t grant implicit trust. Being inside the corporate LAN doesn’t mean a device should be trusted by default. Every request gets evaluated against policy, every time, regardless of where it comes from.
That’s a deliberately narrow, digital-systems standard. It says nothing about who gets through your front door. The NIST document itself doesn’t cover physical access control.
Why Physical Security Has the Same Problem Zero Trust Was Built For
Before zero trust, network security worked on a perimeter model: get inside the firewall, and you’re trusted. Zero trust exists because that model failed, once attackers got past the perimeter, nothing stopped them.
Most office buildings still run on the physical version of that same old model. Clear the front desk, and you’re trusted for the rest of your visit. Nobody checks again. A handful of security practitioners and vendors, RightCrowd, Trackforce, and SecurityInfoWatch among them, have spent the last few years making exactly this argument: the assumption that broke network security is the same assumption still running most physical security. It’s a growing industry conversation, not an official standard extension, but the parallel holds up.
Three Zero-Trust Principles, Applied to Visitors and Contractors
Verify explicitly, every time. A visitor who checked in cleanly last month isn’t automatically safe this time. Watchlist screening belongs at every check-in, not just the first one, and identity should be confirmed at the door, not assumed because a face looks familiar.
Least-privilege access. A badge that opens every door in the building, issued to a visitor who only needs the second floor, is the physical version of giving someone admin rights they’ll never use. Scoping a contractor’s access to a specific zone and time window is the practical version of this principle, not a building-wide badge handed out by default.
Assume breach, monitor continuously. Zero trust assumes something will eventually get through, and builds monitoring around that assumption instead of hoping prevention is perfect. Physically, that means a real-time, tamper-proof log of who’s where, host notifications the moment someone arrives, and a temporary credential that expires on its own instead of staying active until someone remembers to revoke them.
Where a Manual Process Can’t Keep Up
A sign-in sheet or a front-desk person’s memory can’t enforce any of these three principles at scale. Rechecking every visitor against a watchlist by hand doesn’t happen consistently. A badge printed once doesn’t expire itself. Nobody’s reviewing a paper log in real time during an actual incident. These aren’t failures of the people running the front desk, they’re structural limits of a manual process being asked to do a job it was never built for.
The Honest Limit of This Analogy
Zero trust is a real, specific, documented standard for digital infrastructure. Extending its language to physical security is a useful way to think about the problem, not a claim that your lobby is now NIST-compliant. Treat it as borrowed logic, not a certification, and the distinction matters if a security review ever asks exactly what standard you’re claiming to meet.
Where Vizitor Fits
Vizitor applies the same three principles concretely. Every visitor is checked against a watchlist at every check-in, with ID capture and OTP verification, rather than relying on recognition from a past visit. Access can be scoped to authorized zones and time windows, so a contractor’s badge works where and when it’s supposed to and nowhere else. Audit-ready logs track every entry, exit, and document in real time, and host notifications fire the moment a guest arrives rather than relying on someone checking a desk periodically. None of this requires calling it zero trust to be worth having, it’s just what explicit verification and least-privilege access actually look like at a front desk.
See Explicit Verification at Every Check-In
Watch how Vizitor screens, scopes, and logs every visitor and contractor, not just at the first visit.
Frequently Asked Questions
See Vizitor in action check-in a visitor in under 30 seconds
Trusted by 500+ businesses. QR check-in, badge printing, NDA signing. Plans from $36/mo.